Our services
The master keys to the business, found, vaulted, rotated and logged, without a day of disruption.
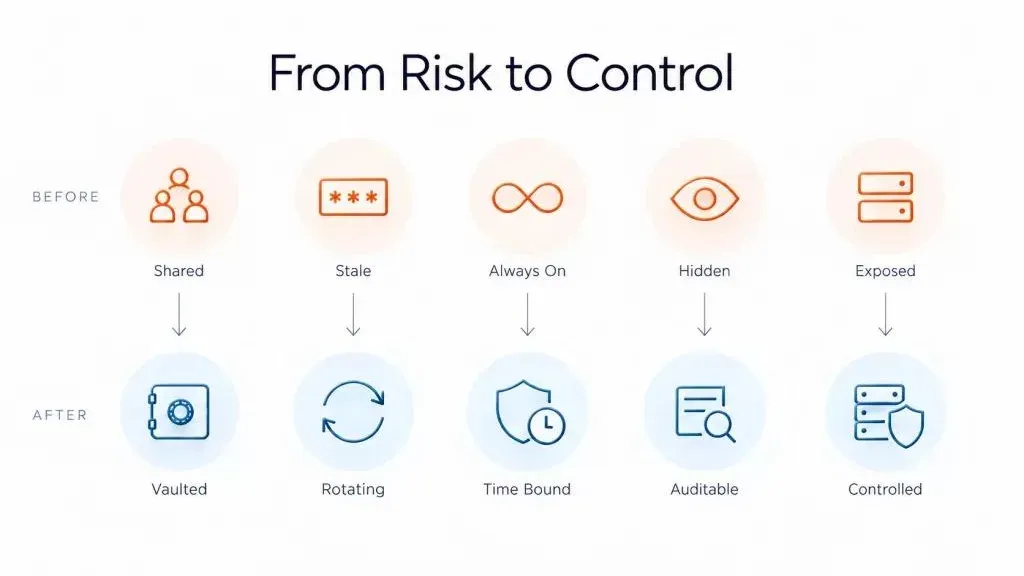
Administrative and service accounts carried elevated permissions and worked like master keys to the environment. Many were shared, stale or invisible.
A privileged access program that covers every elevated account, including the legacy ones.
Account discovery
We identified and inventoried every elevated account: shared and individual admin accounts, service accounts, system-level accounts and legacy platform accounts.
Credential vaulting
All privileged credentials moved into a protected vault, so nobody needs to store or share static passwords.
Password rotation
Passwords change automatically after checkout or on a schedule, removing long-lived static credentials.
Legacy protection
Systems that cannot support MFA are reached through controlled jump hosts and limited sessions.
Time-bound access
Privileged access is granted to approved users for approved periods and expires automatically.
Activity logging
Every privileged access event is recorded for security and regulatory review.
Tell us what you run and get a clear quote that lists every user, server and device we would cover.